

Rule-Based WAF #
In addition to the ML-based engine, the Check Point-powered WAF includes a standard rule-based engine called Intrusion Prevention (IPS), which can prevent suspicious activity based on predefined security rules.
IPS provides protection for over 2,800 web-based CVEs (Common Vulnerabilities and Exposures), including vulnerabilities associated with the OWASP Top 10, as well as additional rules designed and maintained by Check Point.
Security signatures are automatically delivered to agents and gateways as soon as they are released by the Check Point Security Research team.
For example, IPS provides protection against:
- SQL injection
- Path traversal
- LDAP injection
- Evasion techniques
- Illegal HTTP methods
- Log4Shell
- Text4Shell
- MOVEit-related attacks
One specific benefit of these signatures is the ability to view logs that identify the specific CVE number associated with a detected threat.
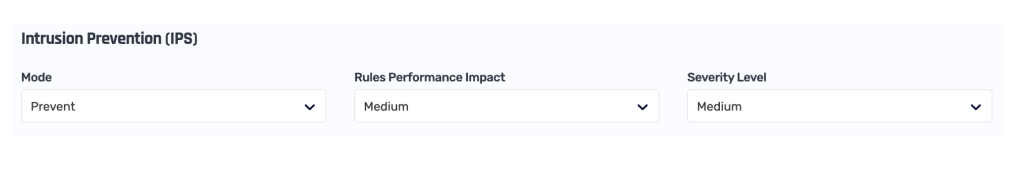
Like the ML-based engine, the rule-based engine supports different operating modes:
- Learn – The initial mode. The engine analyzes traffic but does not block requests.
- Prevent – The engine blocks traffic according to its configured rule set.
- Disabled – Completely disables the rule-based engine.
Rules Included #
IPS includes rules covering threats such as those described in the OWASP Top 10, including:
- Broken Access Control, for example:
- Bypassing access control checks by modifying the URL, such as through parameter tampering or forced browsing.
- Elevation of privilege.
- CORS misconfiguration.
- Forced browsing by guessing URLs.
- Security Misconfiguration, for example:
- Missing appropriate security hardening.
- Missing security headers or directives, or headers and directives that are not configured with secure values.
- Injection, such as:
- SQL injection.
- OS command injection.
- LDAP injection.
- Authentication Failures, such as:
- Credential stuffing, with or without password spraying attacks.
- Weak or commonly used passwords.
- Session identifiers exposed in URLs, hidden fields, or other insecure locations.
Configuration #
IPS Overhead #
The engine includes a large set of rules classified according to their Severity Level and Confidence.
You can control which rules are evaluated and activated to manage the performance impact on your traffic. Activating more rules increases CPU usage because each active rule must be evaluated for every request.
You can control this in two ways:
- Set the Performance Impact you are willing to sustain, ranging from Low (fewer rules activated) to High (more rules activated).
- Set the rules’ Severity Level, ranging from High (only rules for high-severity threats are activated, resulting in fewer active rules) to Low (all applicable rules are activated, resulting in more active rules).
IPS Threat Prevention and Confidence Levels #
While the engine is in Learn mode, it does not block traffic. Instead, suspicious activity is added to the WAF engine’s sampled logs.
Once the engine is set to Prevent mode, you can control which rules are applied by configuring its behavior for:
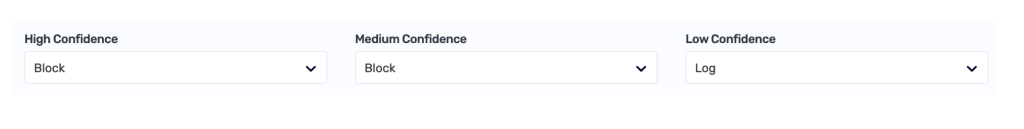
- High Confidence
- Medium Confidence
- Low Confidence
We recommend starting by enabling prevention for High Confidence rules.